
Crypto KYC requirements mean collecting and verifying a customer's legal name, date of birth, address, and government-issued ID, tied to ongoing anti-money laundering (AML) and customer due diligence (CDD) obligations. Most platforms also run sanctions and politically exposed person (PEP) screening as standard. The immediate action for any exchange, wallet provider, or individual onboarding onto a regulated platform is to prepare that documentation in advance and, at the business level, adopt a documented, risk-based verification programme rather than a flat checklist.
What crypto KYC verification actually requires
KYC in crypto works the same way it does in traditional banking. It exists to satisfy AML and CDD obligations, not merely to slow you down at sign-up. Platforms need to know who they are transacting with, where the funds came from, and whether that person or entity appears on a sanctions or watch list.
The core data set is consistent across most regulated platforms: full legal name, date of birth, residential address, and a government-issued identity document such as a passport, driving licence, or national ID card. Proof-of-address documents (utility bills, bank statements, tenancy agreements) are usually accepted only if dated recently.
Verification has become largely automated. Platforms typically run:
- Optical character recognition (OCR) to extract and cross-check data from the submitted document
- Near-field communication (NFC) chip reads on biometric passports and ID cards to confirm authenticity
- Selfie and liveness checks to match the applicant's face to the document photo and rule out spoofing
- Device fingerprinting to flag accounts linked to previously blocked devices or suspicious IP ranges
- Sanctions and PEP screening against global watch lists, run at onboarding and again on a recurring basis
Pro Tip: Submit documents in good lighting against a plain background. Document quality is one of the leading causes of failed verification, and a blurry photo will bounce even a valid, unexpired ID.
The reason platforms stack multiple checks rather than relying on a single document scan is straightforward: identity fraud rings target crypto onboarding specifically, and no single check catches every fabrication method on its own.
Who must comply and which services trigger KYC obligations
Not every crypto service carries a KYC obligation, and the boundary matters enormously for structuring.
Operators that typically fall squarely within scope include:
- Centralised exchanges (CEXs) handling fiat-to-crypto or crypto-to-crypto trading
- Custodial wallet providers holding private keys on a customer's behalf
- Fiat on-ramps and off-ramps converting between traditional currency and digital assets
- Brokerages and over-the-counter (OTC) desks facilitating trades on a client's behalf
Services that commonly sit outside operator-led KYC duties include non-custodial wallets and permissionless smart contracts, where no intermediary controls the assets or facilitates the transaction. That exemption is narrower than many founders assume. The moment a protocol adds a bridge, a custody layer, or a fiat settlement rail, it usually starts to resemble a regulated financial service and inherits the associated obligations.
In the United States, the compliance stack layers global standards over domestic rules: the Financial Action Task Force (FATF) sets international AML expectations, while FinCEN administers the Bank Secrecy Act (BSA), state money transmitter licences (MTLs) apply at the state level, and OFAC sanctions lists constrain who a platform may serve. A business's choice to hold custody, touch fiat rails, or accept corporate clients is what pulls it into this stack, not the label it gives itself.
Tiered verification: how KYC escalates from Tier 1 to Tier 3
Most compliant exchanges and custodians run a three-tier verification model rather than treating every customer identically. Zyphe's analysis of exchange onboarding describes this structure as the standard approach across the industry.
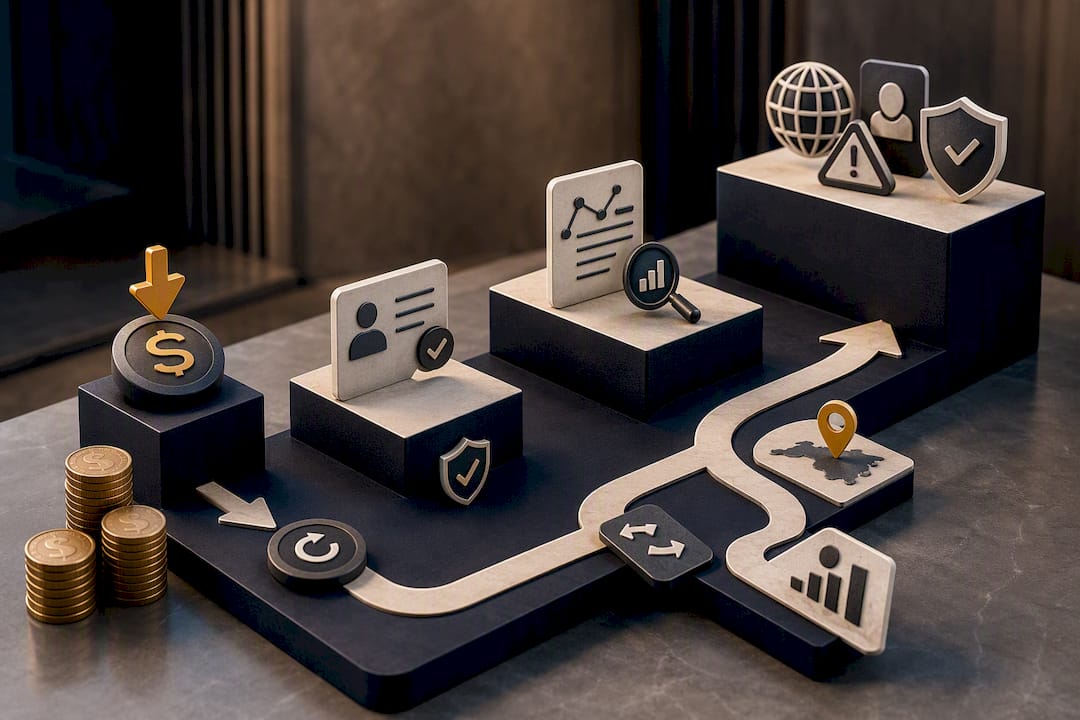
- Tier 1: minimal verification. Email and phone confirmation plus device fingerprinting, usually sufficient only for view-only accounts or very low transaction limits.
- Tier 2: full identity verification. Government-issued ID, selfie and liveness matching, address verification, and baseline sanctions/PEP screening. This tier unlocks standard trading and withdrawal limits.
- Tier 3: enhanced due diligence (EDD). Source-of-funds and source-of-wealth documentation, corporate formation and beneficial ownership records, and named-officer sign-off for high-risk or high-value customers.
Pro Tip: Escalation should never be a static rule tied only to deposit size. A genuinely risk-based programme lets behavioural signals, not just thresholds, decide when a customer moves up a tier.
The trigger for escalation is rarely a single event. A sudden large deposit, rapid movement of funds in and out of an account, transfers involving high-risk jurisdictions, or a mismatch between stated occupation and transaction volume will typically push a customer from Tier 2 into EDD review, regardless of how long they have held the account.
Travel Rule, sanctions screening and transaction monitoring
KYC does not stop at onboarding. Three ongoing controls extend it into the transaction layer itself.
The Travel Rule requires virtual asset service providers (VASPs) to transmit specific counterparty data, originator and beneficiary name, account number, and address, alongside qualifying transfers, based on thresholds set by FATF and relevant regulatory guidance. and reflected in FinCEN's guidance on virtual currencies. That guidance treats transmittal of virtual currency in the same regulatory frame as traditional money transmission, which is why sending platforms cannot simply process a transfer without capturing who is on the other end.
Sanctions screening against OFAC and equivalent lists is a continuous, non-negotiable control, not a one-time onboarding gate. It runs on every customer at intake and again on a recurring basis as lists are updated.
Transaction monitoring, often called know-your-transaction (KYT), watches on-chain and platform activity for patterns that suggest layering, structuring, or exposure to sanctioned wallets. Key components include:
- Real-time screening of deposit and withdrawal addresses against blocklists
- Behavioural analytics flagging deviations from a customer's established pattern
- Automatic alert generation that routes suspicious activity into EDD or a suspicious activity report (SAR)
- Data retention sufficient to reconstruct the full transaction and decision history on request
These three controls feed back into KYC directly. An alert from transaction monitoring is usually what triggers a KYC refresh or an escalation to Tier 3, closing the loop between onboarding data and ongoing risk.
Enhanced due diligence: evidence standards that hold up
Enhanced due diligence applies when a customer's risk profile exceeds standard tolerances, PEP status, unusual transaction patterns, or exposure to high-risk jurisdictions or products are the three most common triggers.
The evidence requested at this stage goes well beyond a passport scan:
- Bank statements covering several months, to corroborate stated income against actual cash flow
- Sale agreements or inheritance documents where a large lump sum needs a credible source
- Payroll records or employer letters supporting salary-based wealth claims
- Corporate formation documents and beneficial ownership (UBO) registers for entity clients
FinCEN's CDD final rule sets the baseline expectation for US-regulated entities to collect and verify beneficial ownership information, and EDD is effectively that baseline applied more rigorously to higher-risk profiles.
The practical challenge is balancing evidential rigour against customer friction. Firms that hold up well under regulatory examination tend to use standardised EDD templates, assign a named compliance officer to each escalation decision, and retain the reasoning, not just the documents, behind every approval or refusal.
Why KYC applications fail and how to pass faster
Most rejections trace back to a handful of avoidable errors.
- Expired documents. A passport or licence past its expiry date is an automatic fail on most platforms.
- Poor image quality. Blurry, glare-affected, or partially cropped photos prevent OCR and facial matching from working. Document clarity is consistently the top driver of failed verification.
- Data mismatches. A name or address that doesn't match across the ID, the proof-of-address document, and the account registration triggers manual review or rejection.
For firms, real-time feedback during upload (flagging a blurry scan before submission, not after a three-day review) reduces false rejects substantially, as does a document-quality check built into the capture flow rather than the back-office queue.
Enforcement exposure when KYC obligations are ignored
Regulatory consequences for weak KYC controls range from civil penalties to criminal prosecution. The Liberty Reserve case remains the clearest cautionary example in the sector: its founder was sentenced to 20 years in a Manhattan federal court for operating an unlicensed money transmitting business built on anonymity rather than verification.
Examiners typically focus on:
- Whether audit trails exist for every onboarding and escalation decision
- Whether escalation logs show a named individual approved each EDD outcome
- Whether transaction-monitoring alerts were resolved and documented, not just generated
Remediation after an adverse finding almost always centres on rebuilding that documentation trail and demonstrating that decisions, not just checks, are traceable to a specific accountable person.
Cryptoverse perspective: designing a defensible KYC programme
Most crypto firms treat KYC as a vendor integration problem: bolt on an identity verification (IDV) tool and call the box ticked. That is the wrong frame, and it is the one that fails examinations.
A defensible programme starts by mapping every obligation, Travel Rule transmission, sanctions screening cadence, EDD triggers, to a specific regulatory instrument and assigning named senior accountability for each. It then builds a genuinely risk-based tiering model, one where escalation rules respond to behavioural signals from transaction monitoring, not just static deposit thresholds. KYT, sanctions screening, and and Travel Rule data transmission need to sit inside the same operating procedure, not three disconnected tools.
Legal counsel earns its fee at the structuring stage, before licensing applications, cross-border expansion, or an enforcement letter forces the issue.
— CRYPTOVERSE
How Cryptoverse Legal Consultancy supports compliance and licensing
Building a KYC and AML programme that survives regulatory scrutiny takes more than software. It takes a legal structure that maps every control back to a named obligation, which is exactly where a specialist crypto law firm earns its keep over a generic compliance vendor.
A specialist legal consultancy advises founders, compliance officers, and boards on VASP licensing, KYC and AML policy drafting, EDD playbooks, and regulatory defence across multiple regulators and numerous crypto-friendly jurisdictions worldwide. An initial engagement typically starts with a scoping call and a compliance healthcheck, reviewing your existing tiering model, documentation trail, and escalation logs against the regulatory instruments that actually apply to your licence type. From there, you receive a quoted scope of work rather than an open-ended retainer. If your platform touches custody, fiat rails, or cross-border customers, readers researching sanctions-adjacent risk may also find value in this cryptocurrency risk management checklist as a starting reference point.
Visit the firm's crypto legal services page to request an initial consultation and scope your compliance programme properly.
FAQ
Is it illegal to buy crypto without KYC?
Buying crypto peer-to-peer or through a non-custodial protocol is not inherently illegal, but using a regulated exchange or fiat on-ramp without completing KYC is not possible in practice, since those platforms are legally required to verify customers before processing transactions.
What is a red flag during KYC verification?
Common red flags include mismatched personal details across submitted documents, an ID that fails NFC chip or liveness checks, sudden large deposits inconsistent with account history, and connections to sanctioned or high-risk jurisdictions.
Can I buy crypto without KYC?
Some decentralised exchanges and peer-to-peer platforms allow trades without operator-led KYC, but this comes with reduced buyer protection, lower transaction limits on many platforms, and no recourse if a counterparty disappears.
How do I complete KYC for crypto?
Submit a valid government-issued ID, a recent proof-of-address document, and a selfie for liveness matching, ensuring all details match exactly across every document you provide.